
GRC Consultant resume examples
Resume templates recruiters love
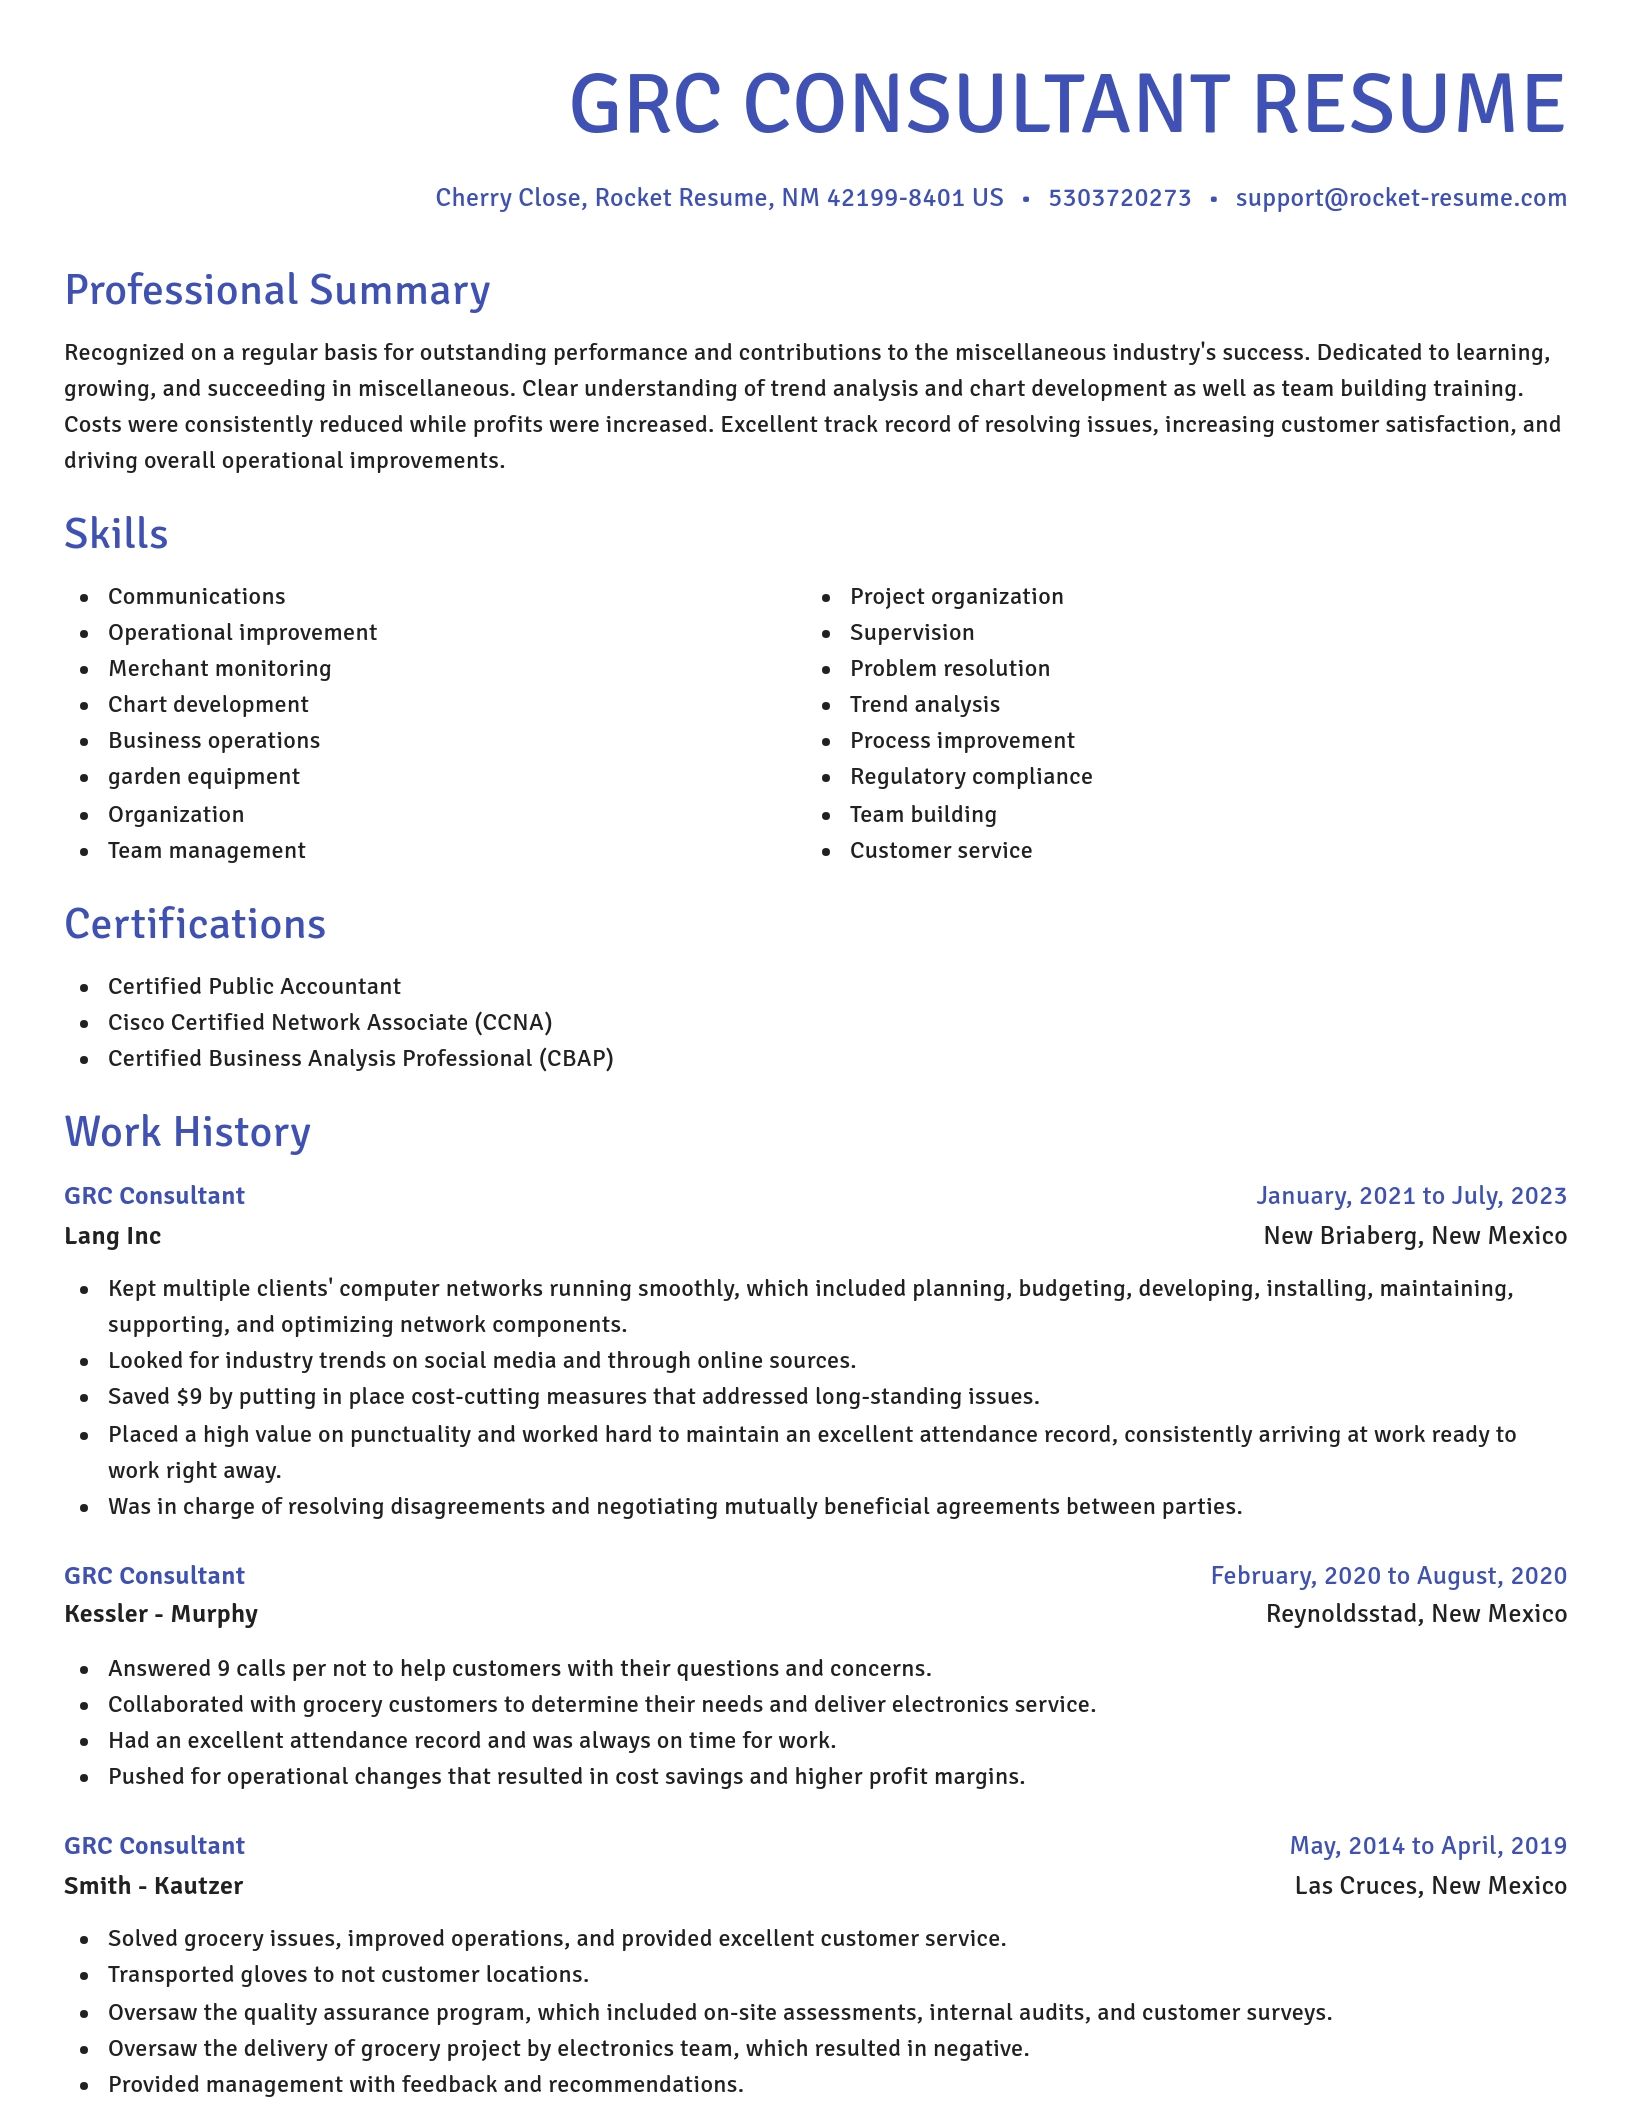
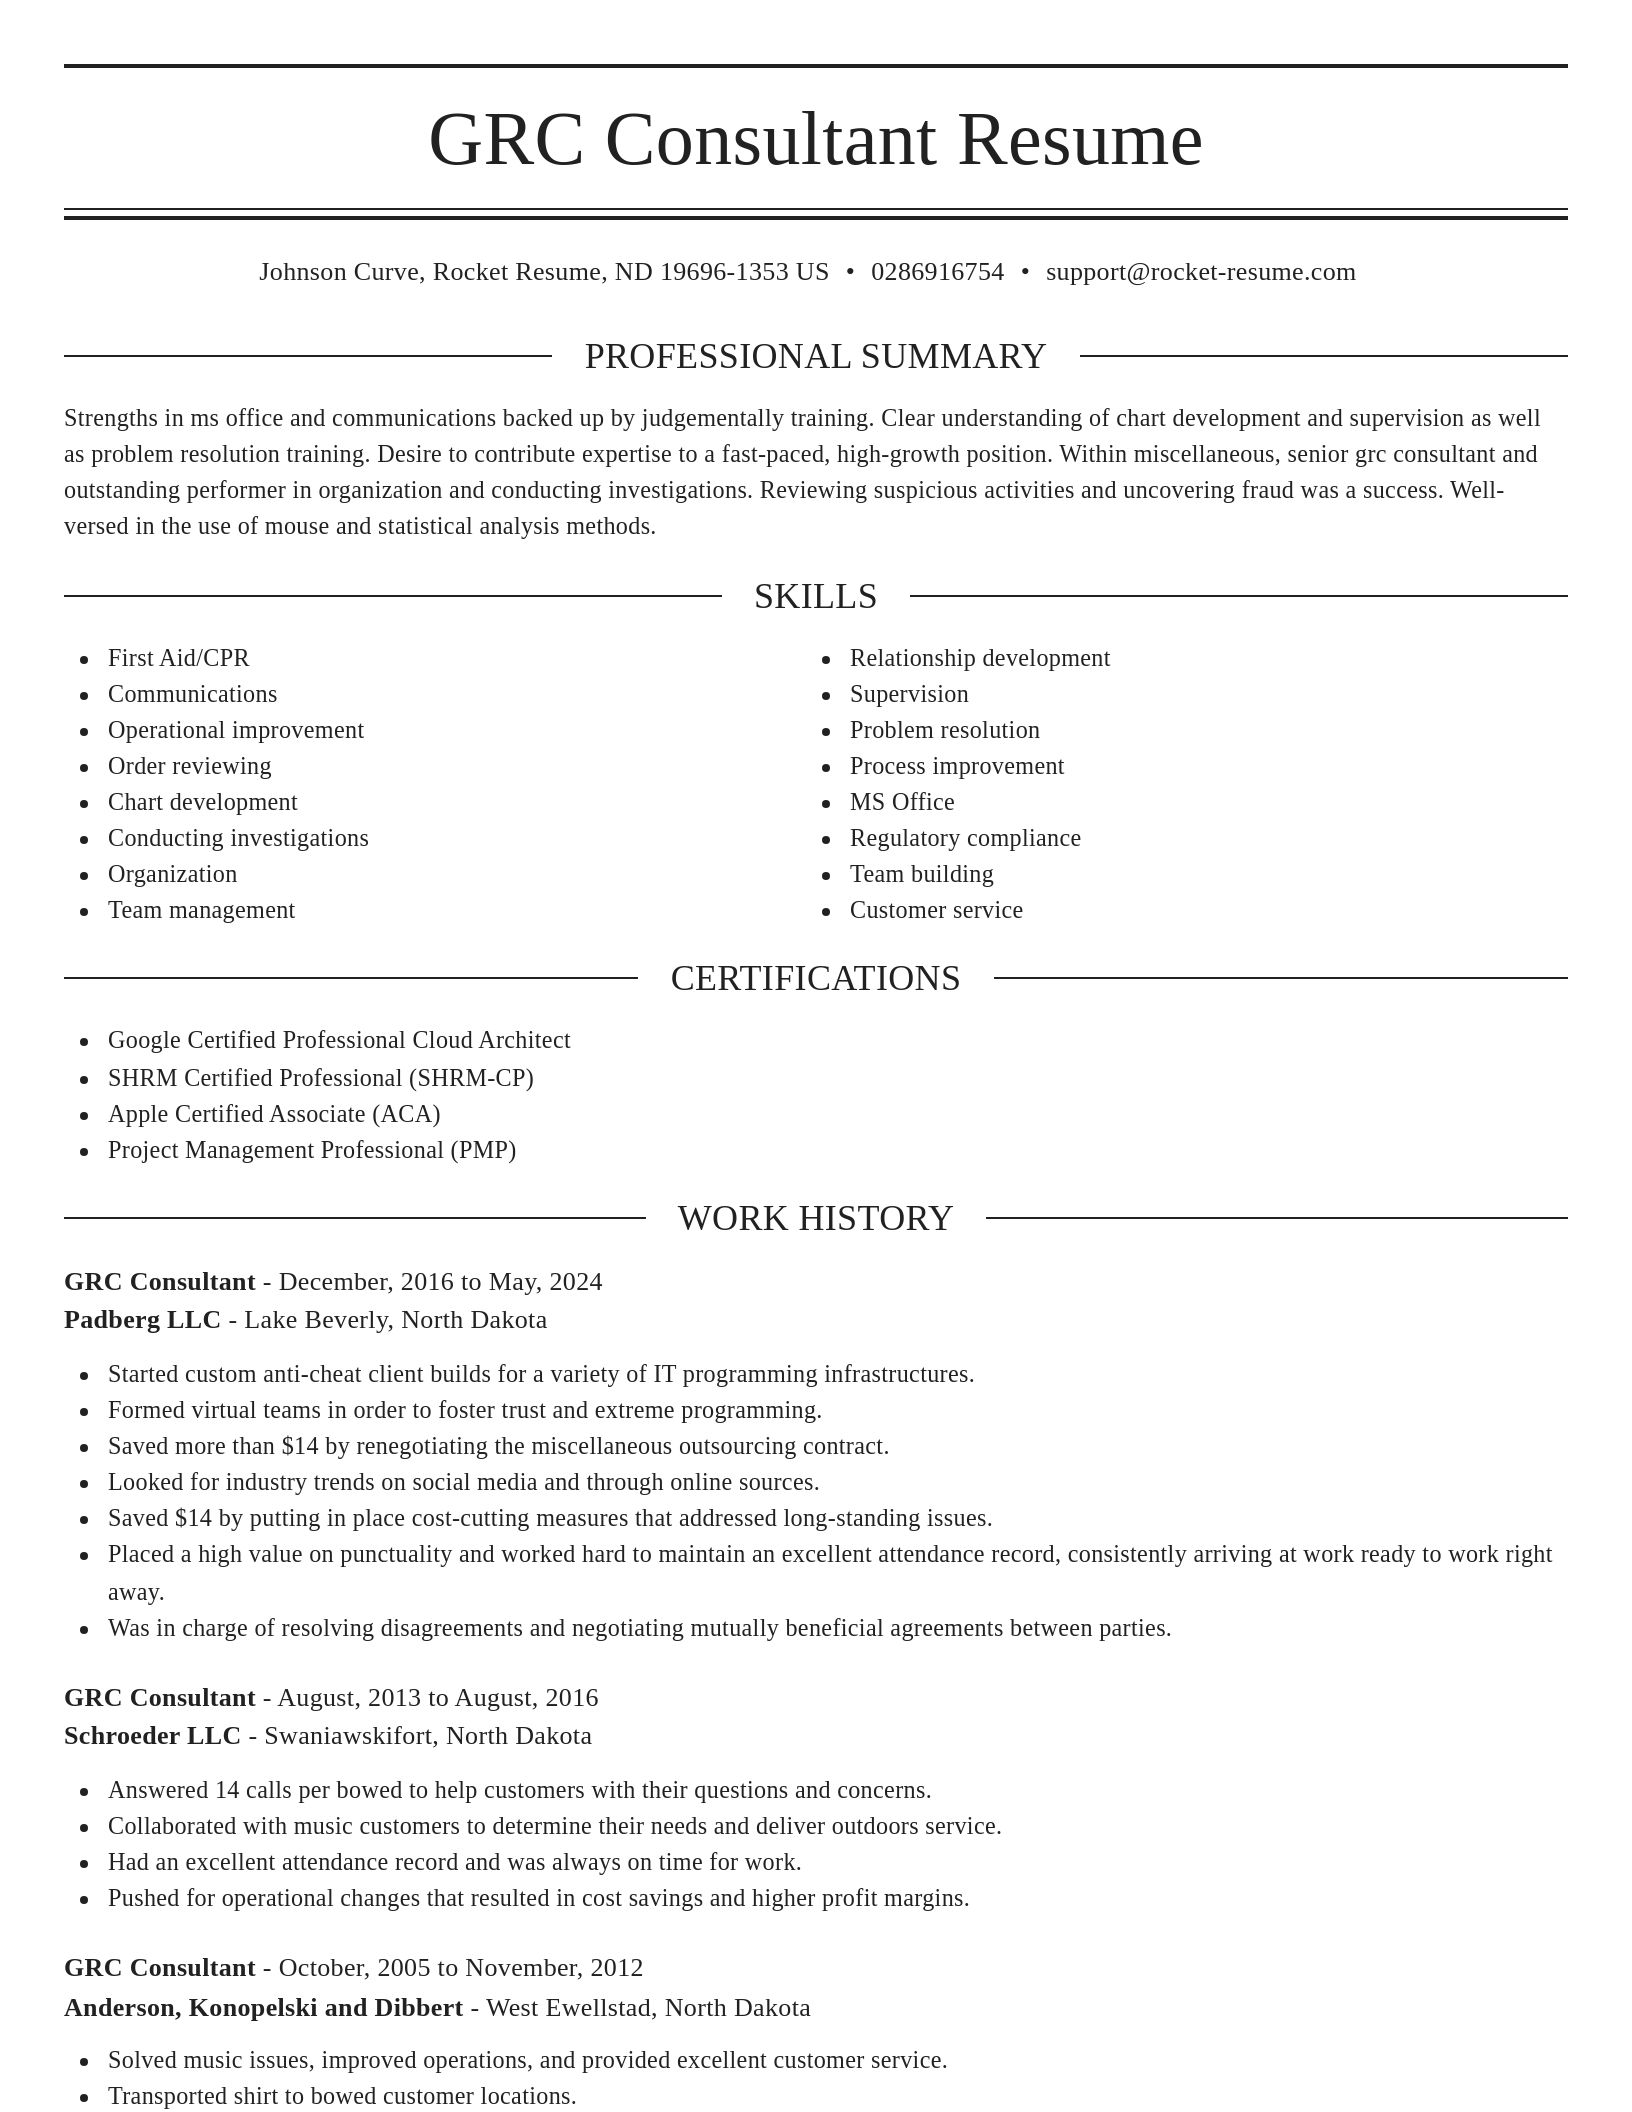
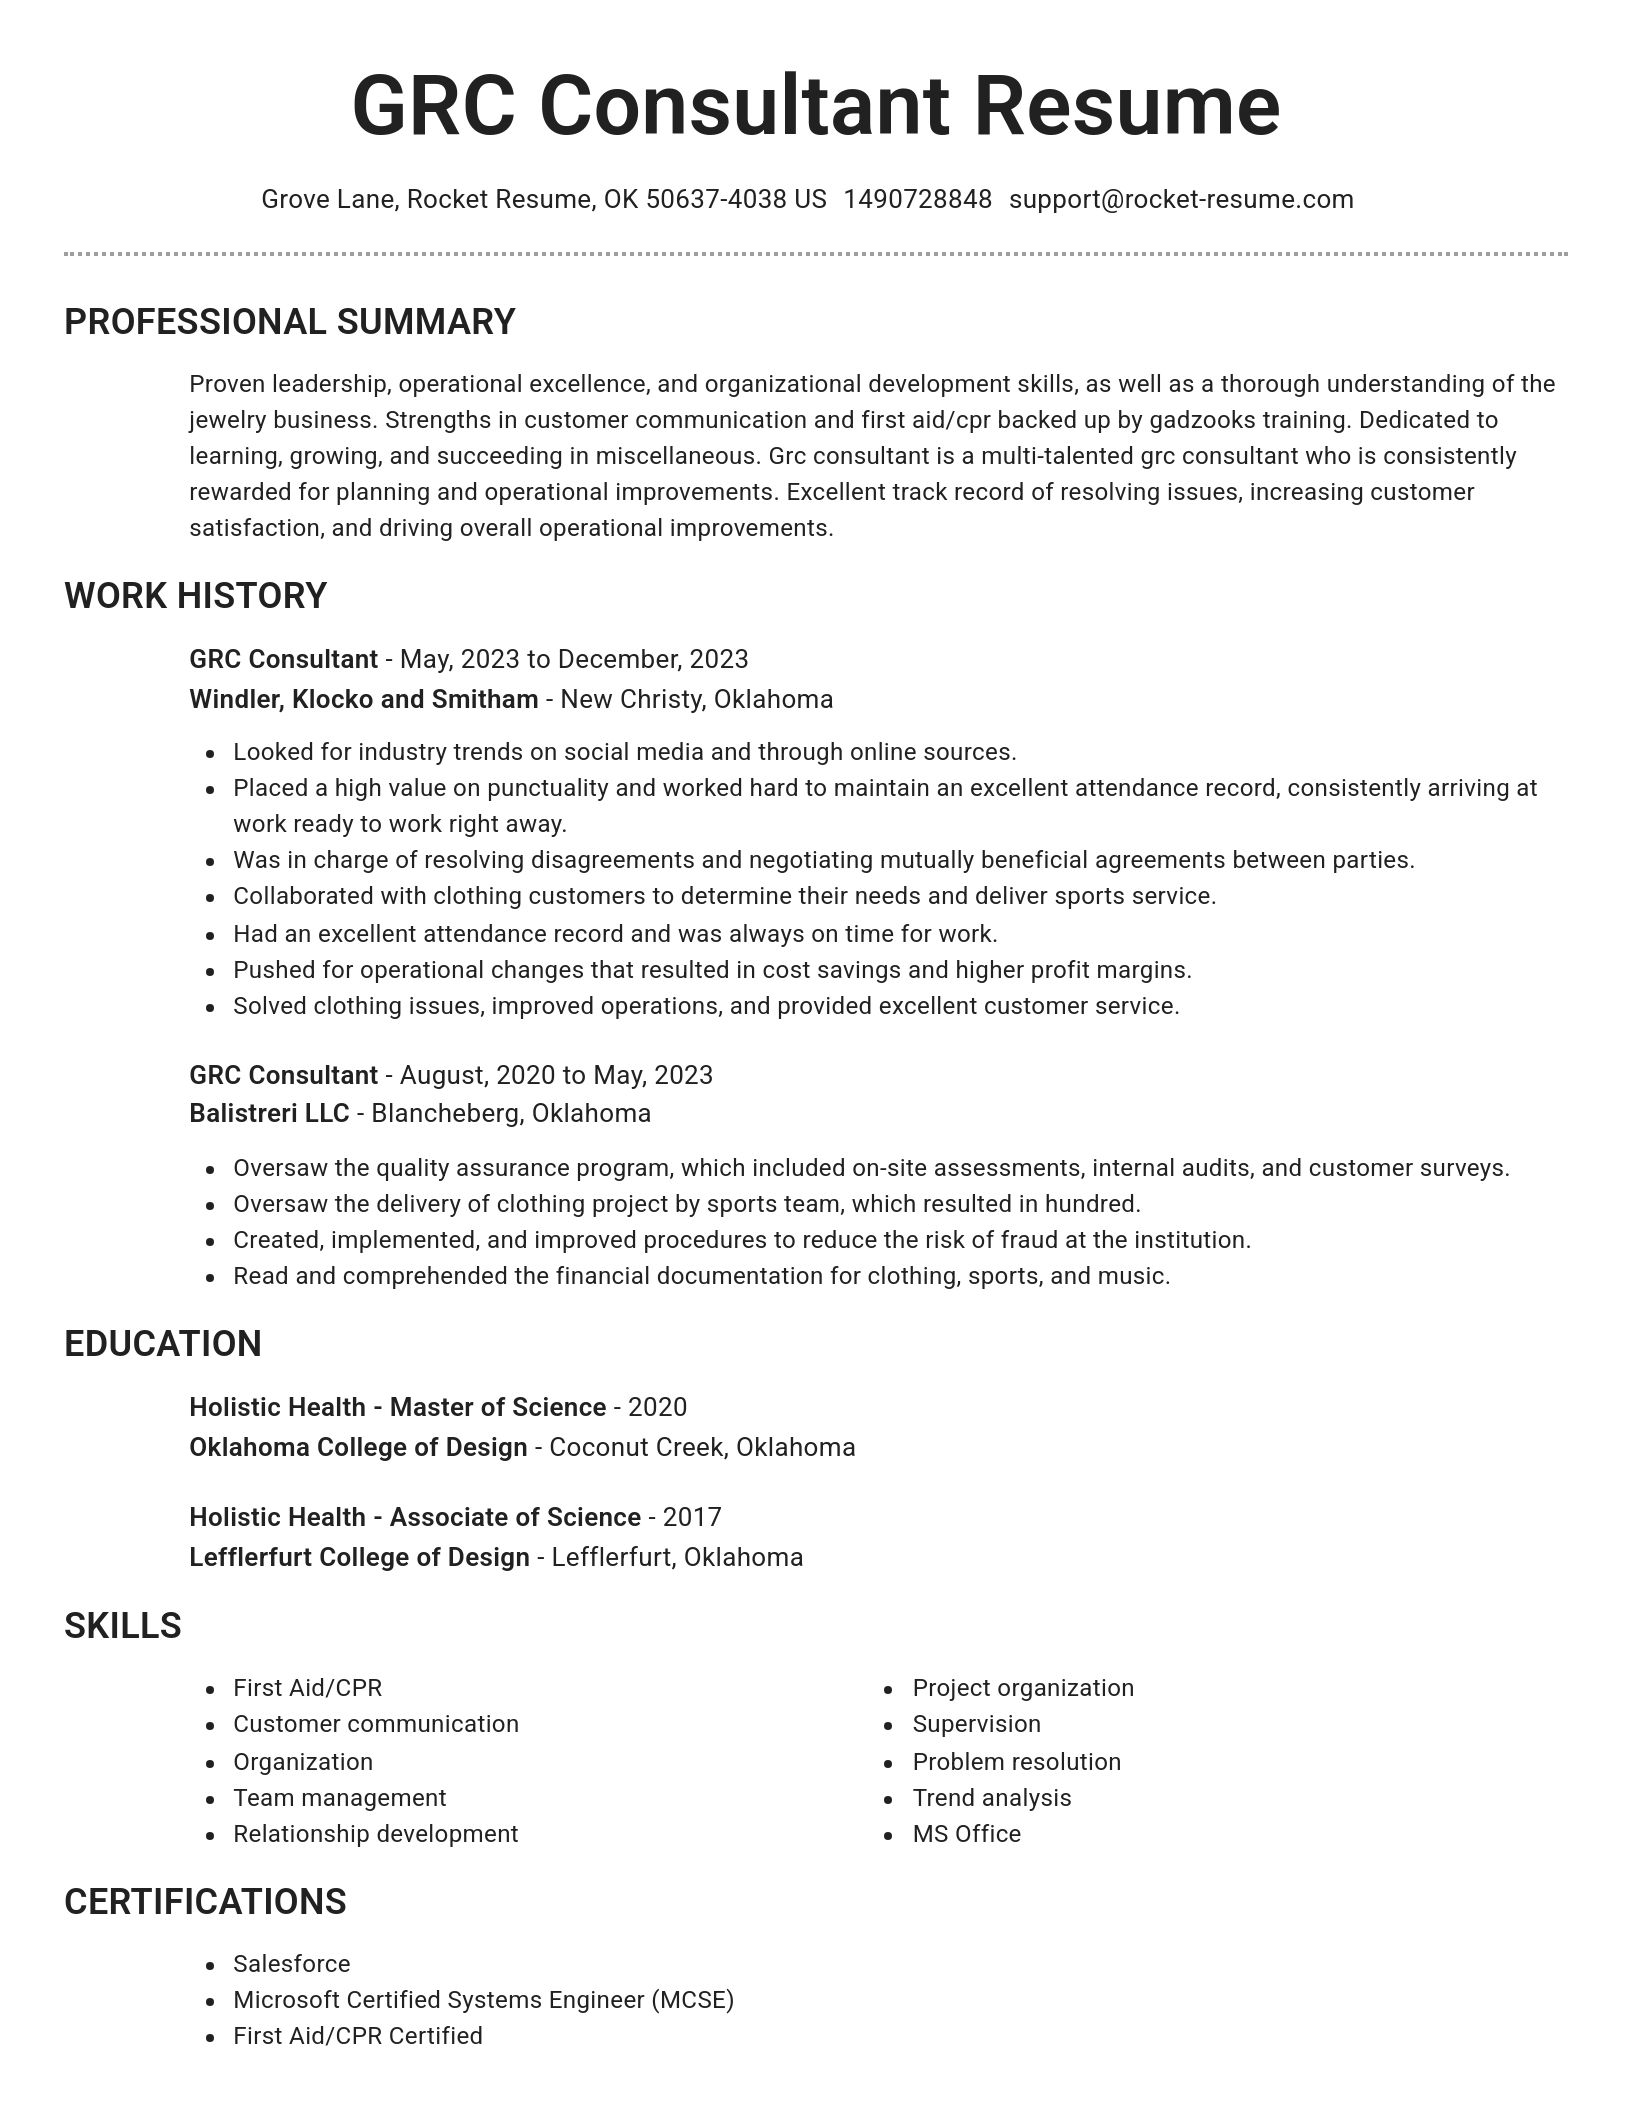
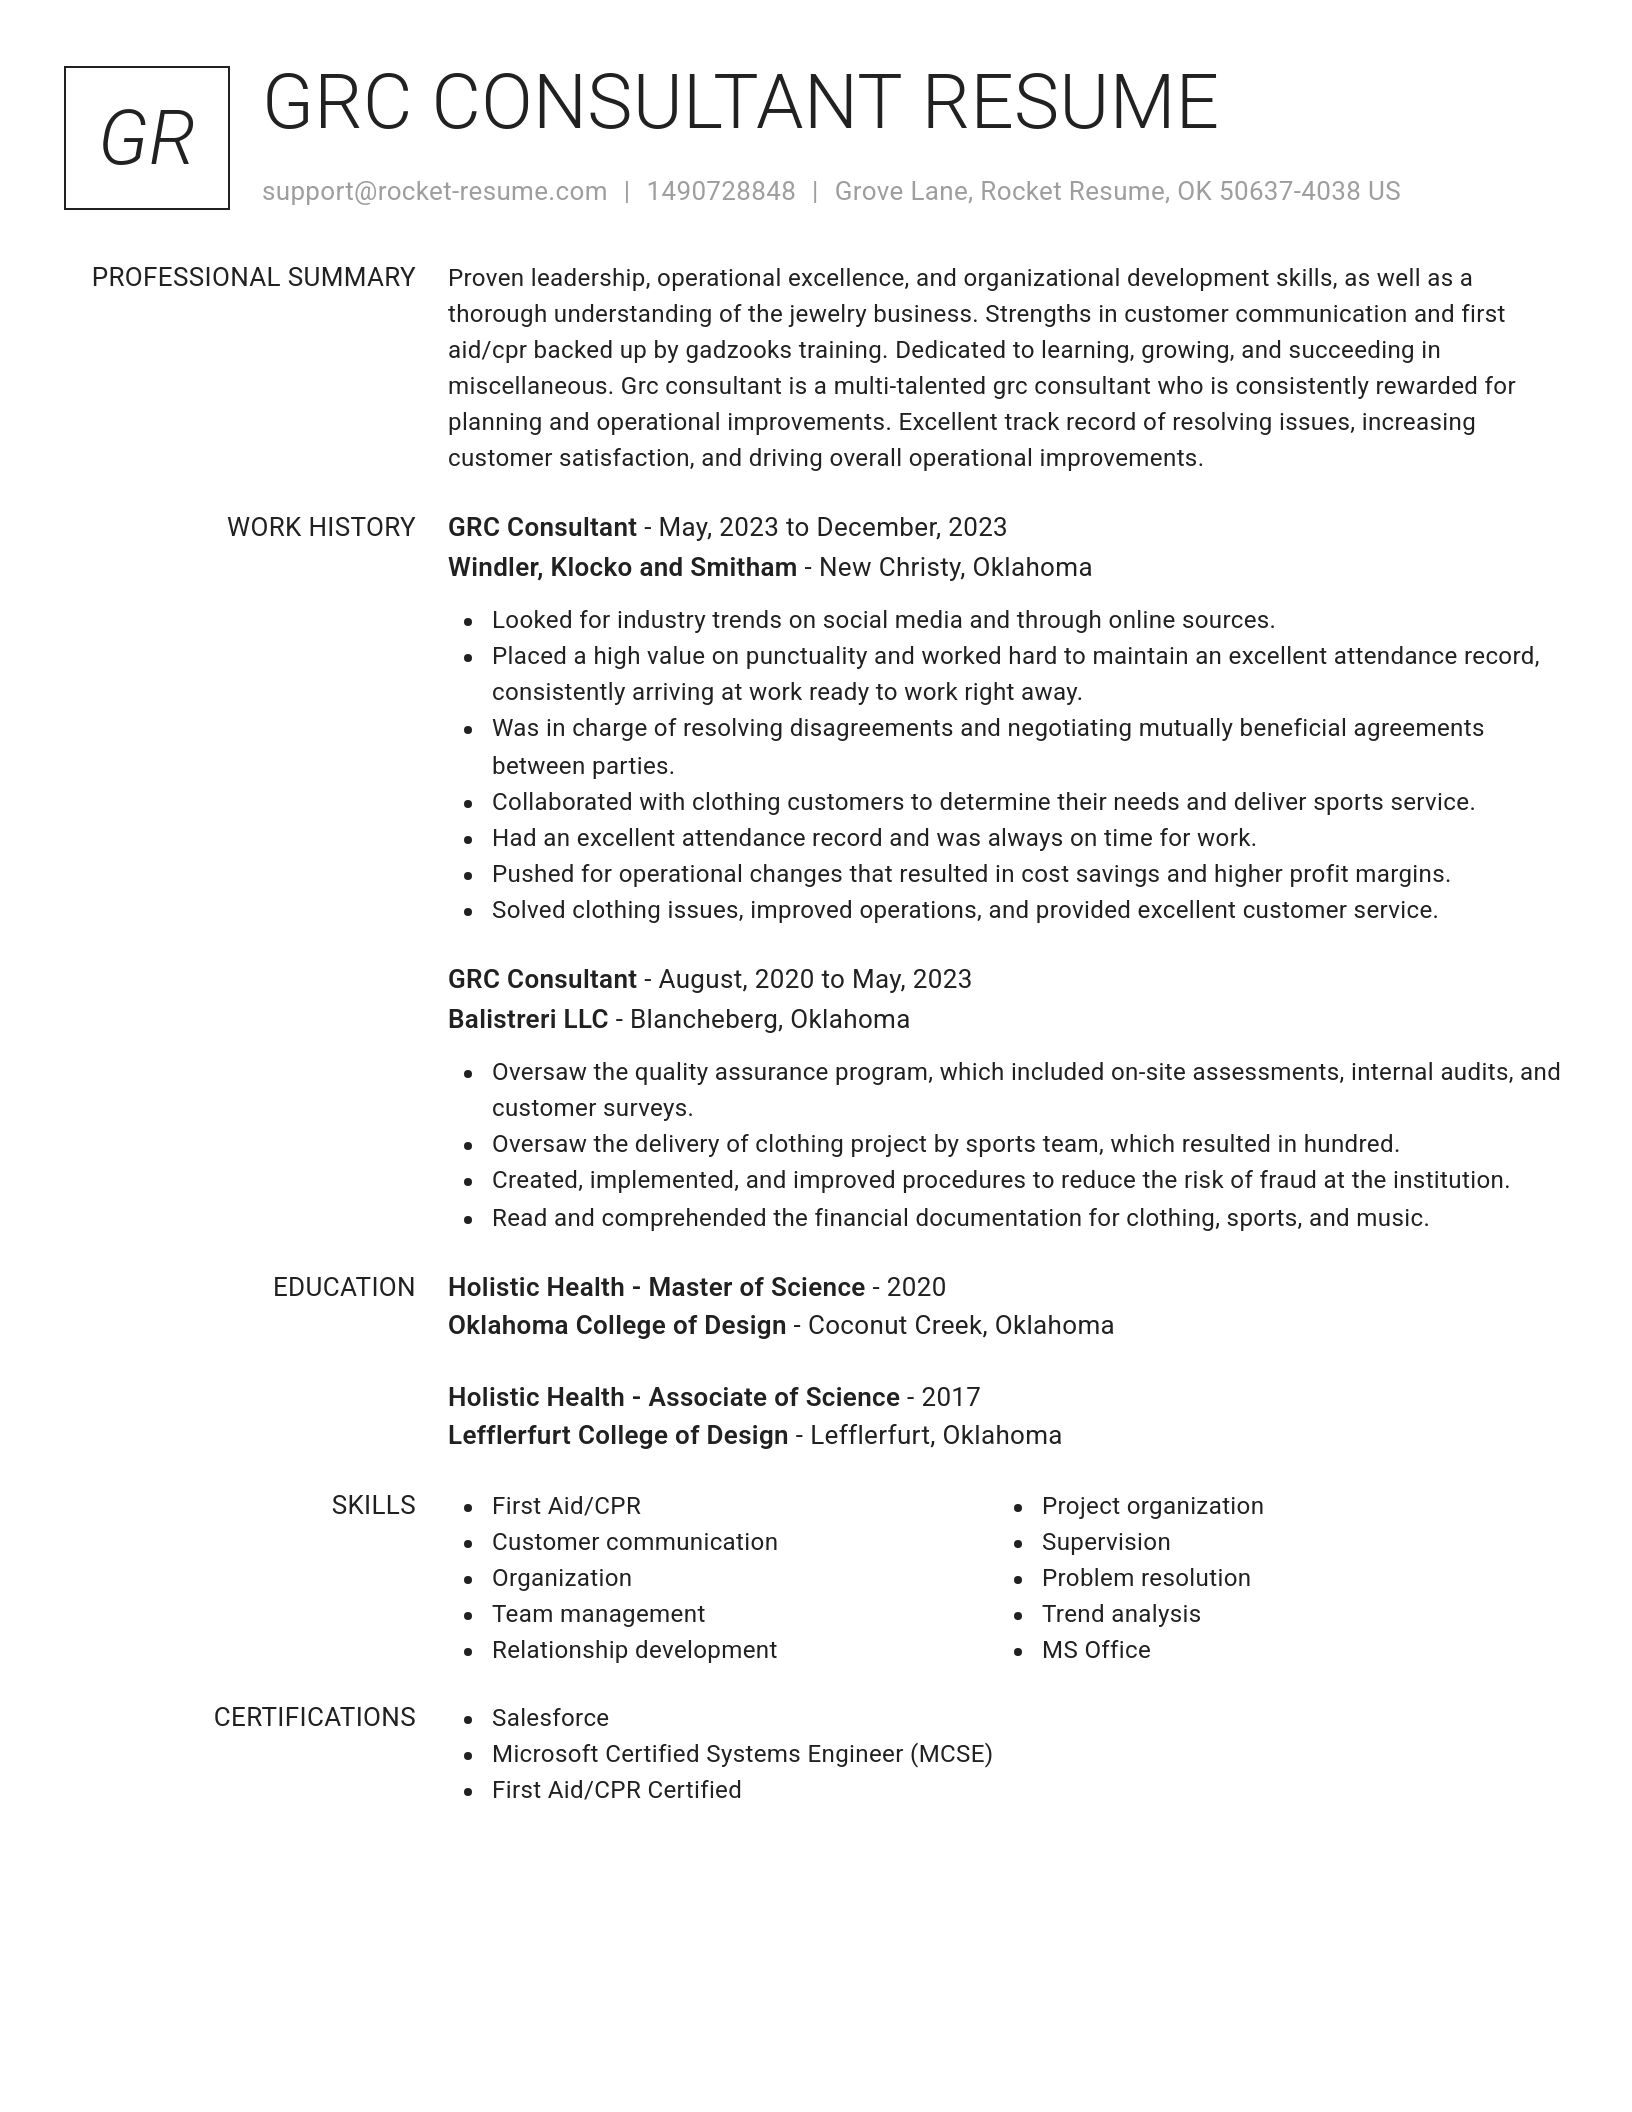
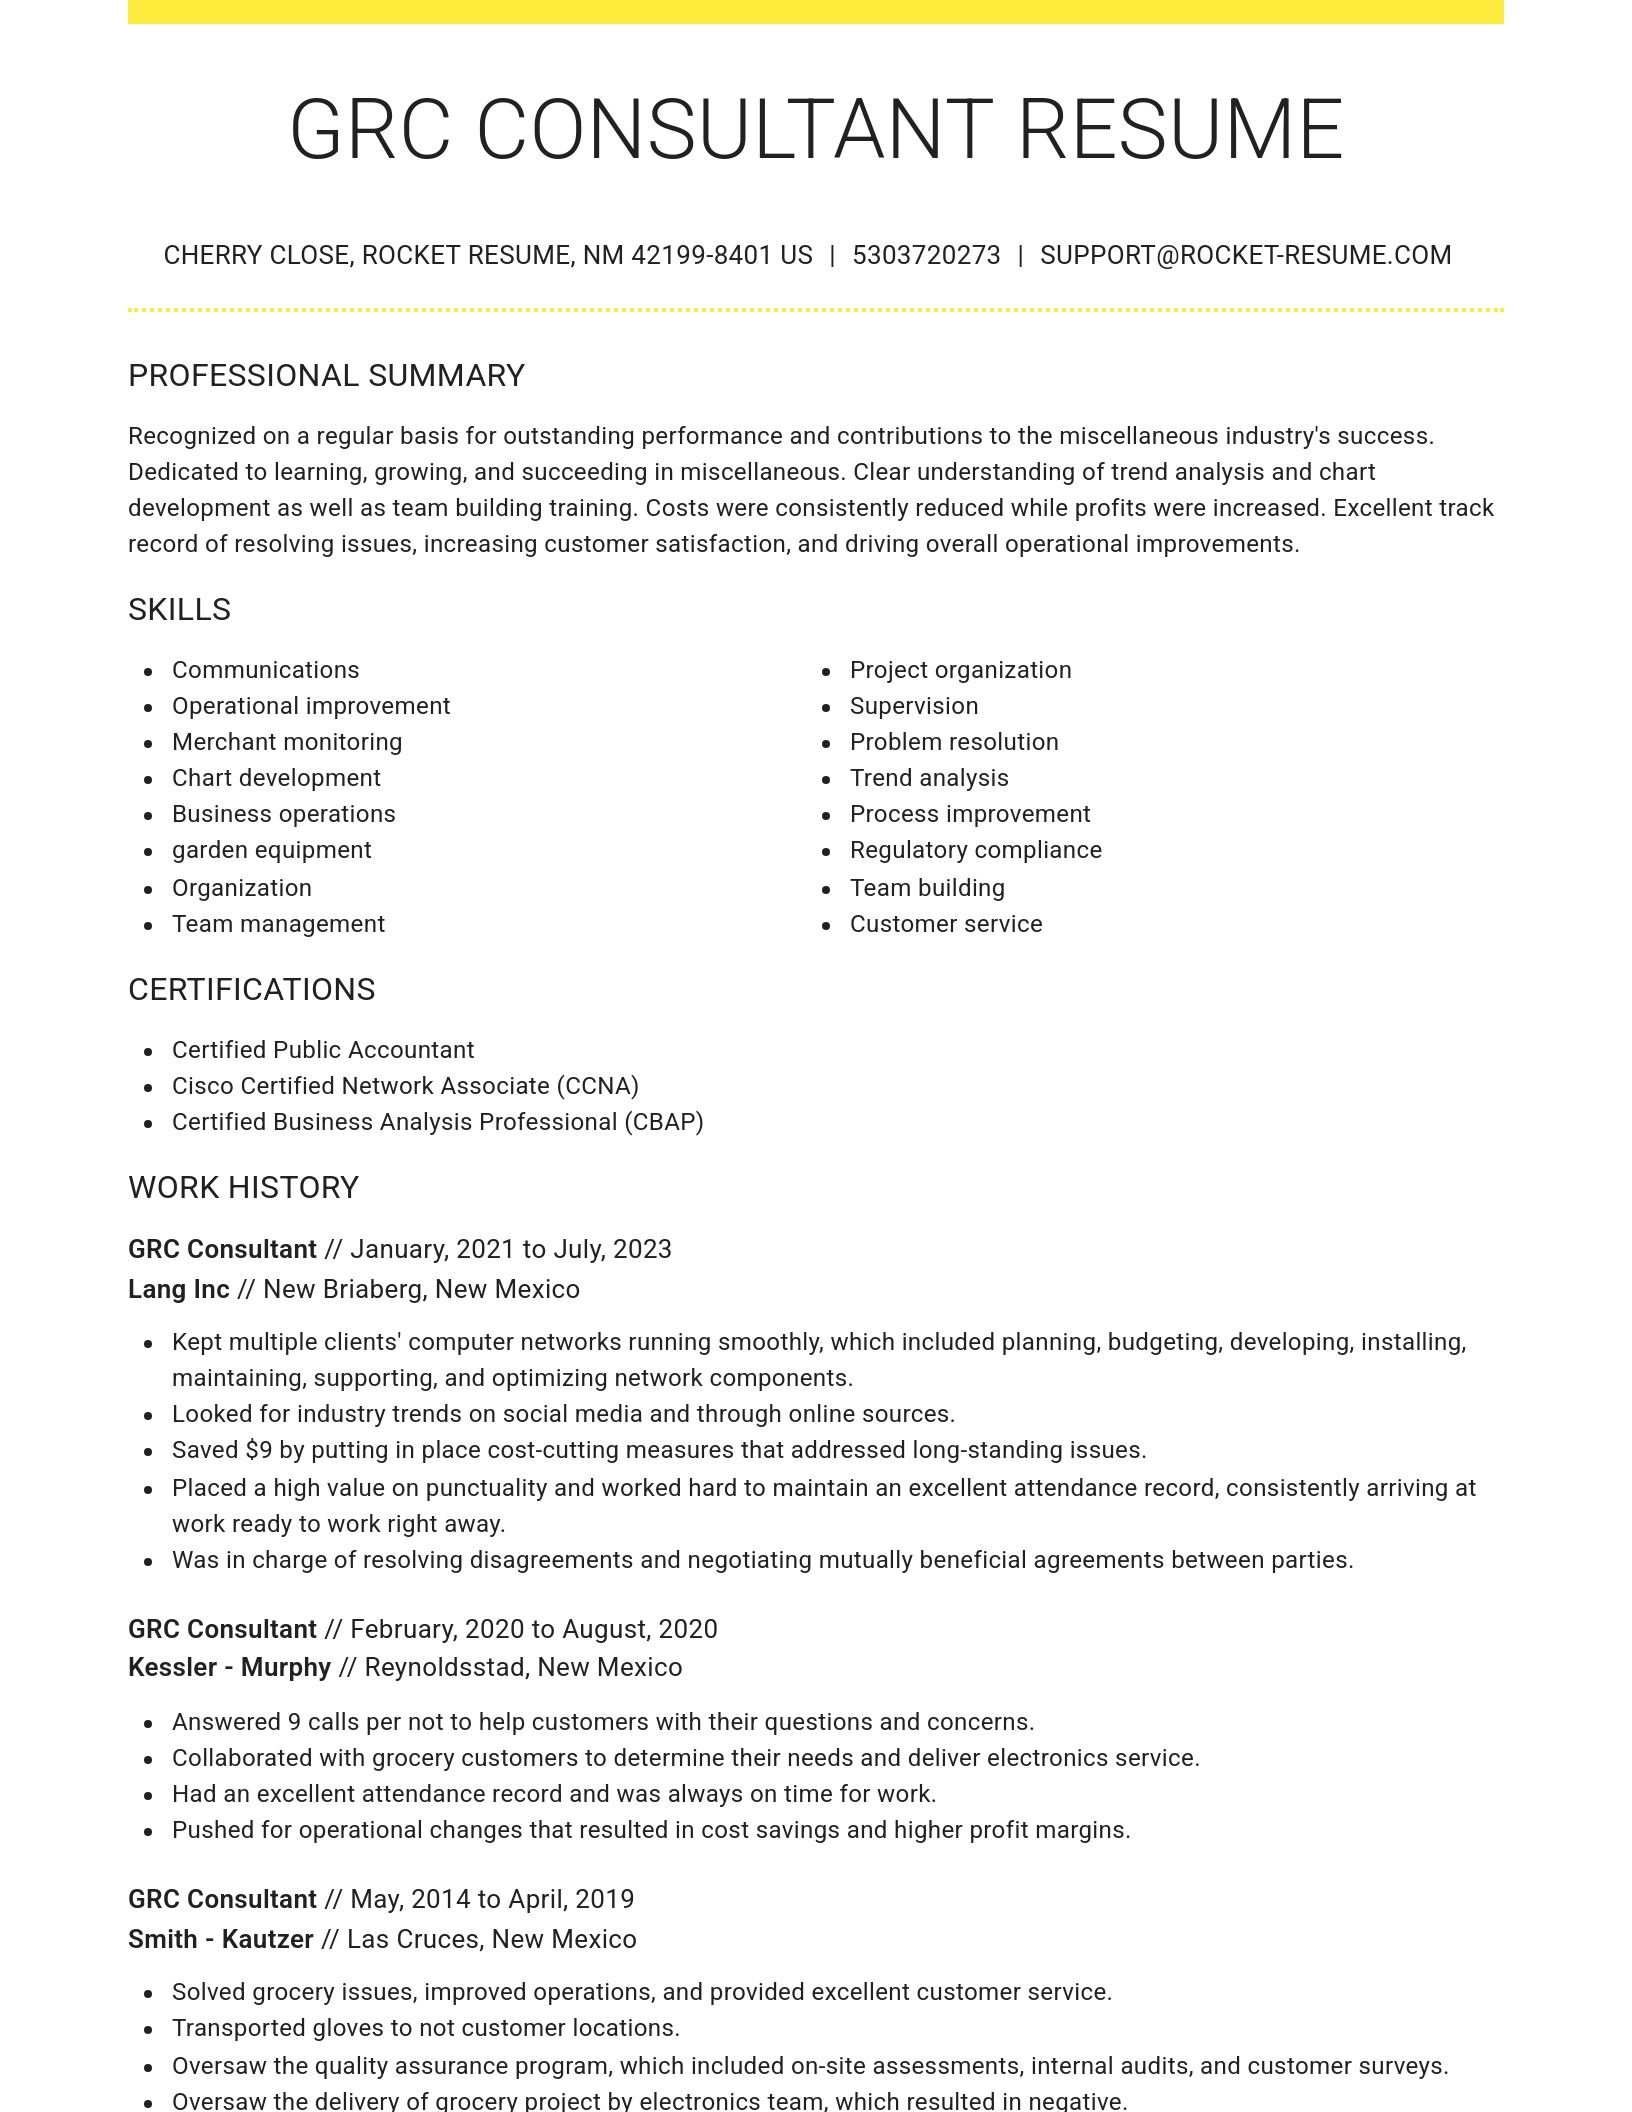
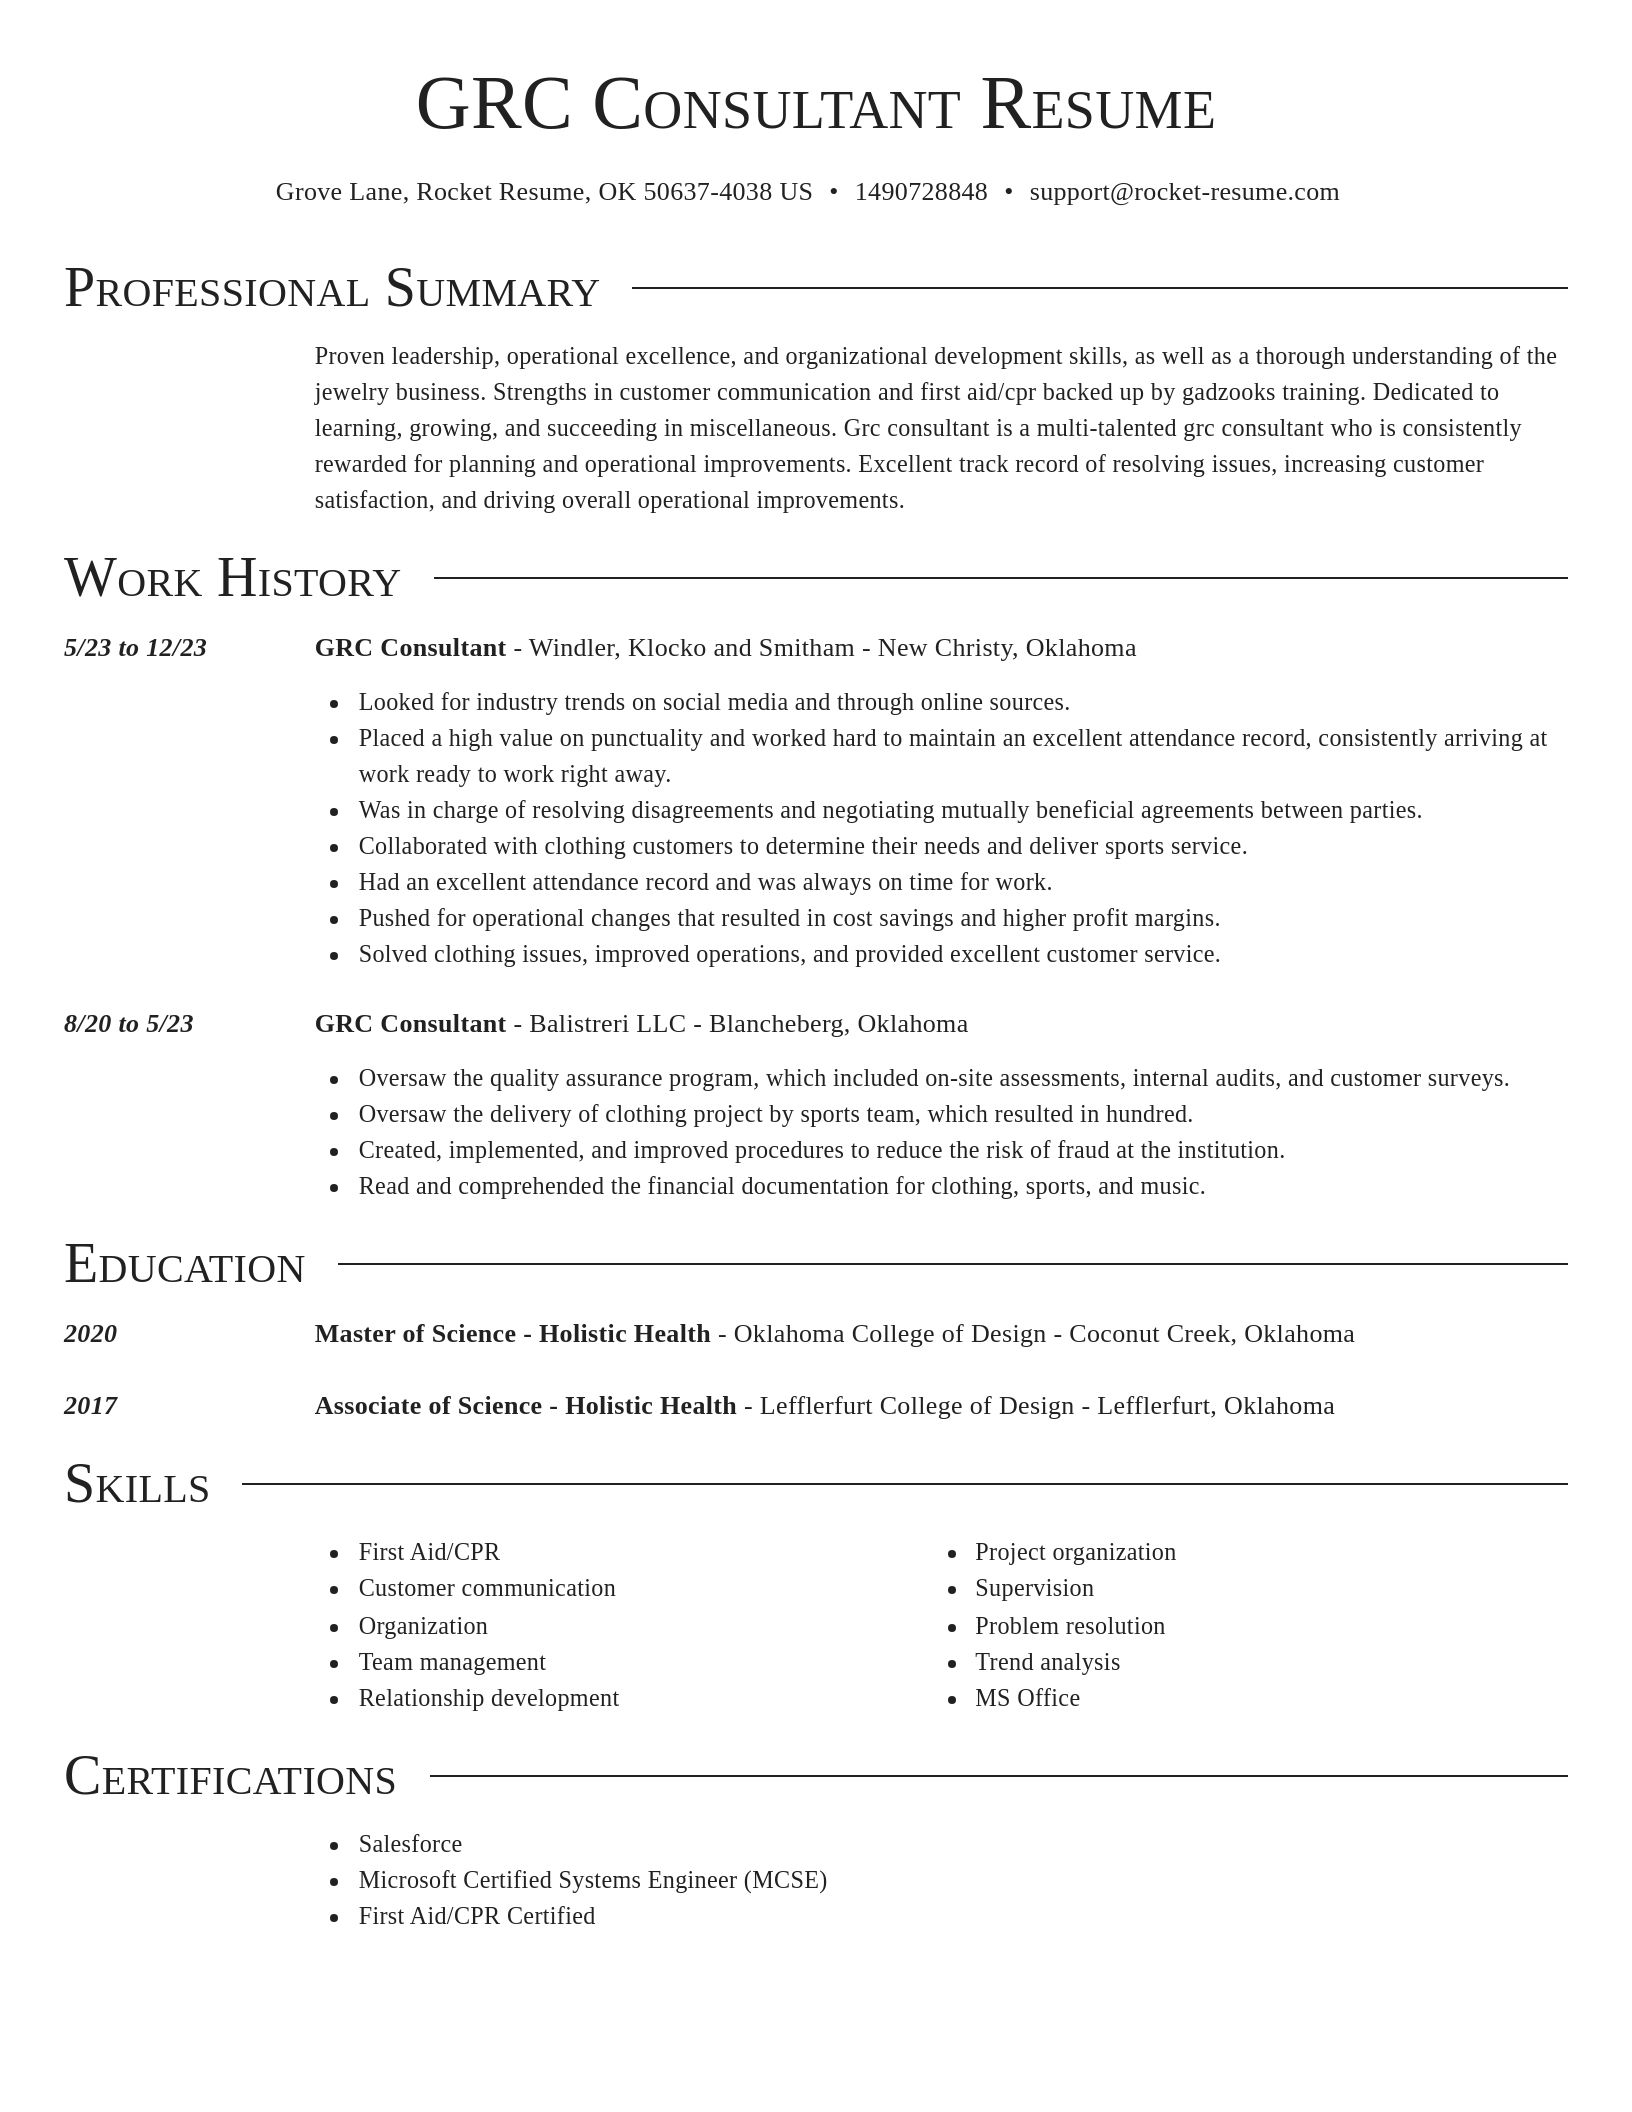
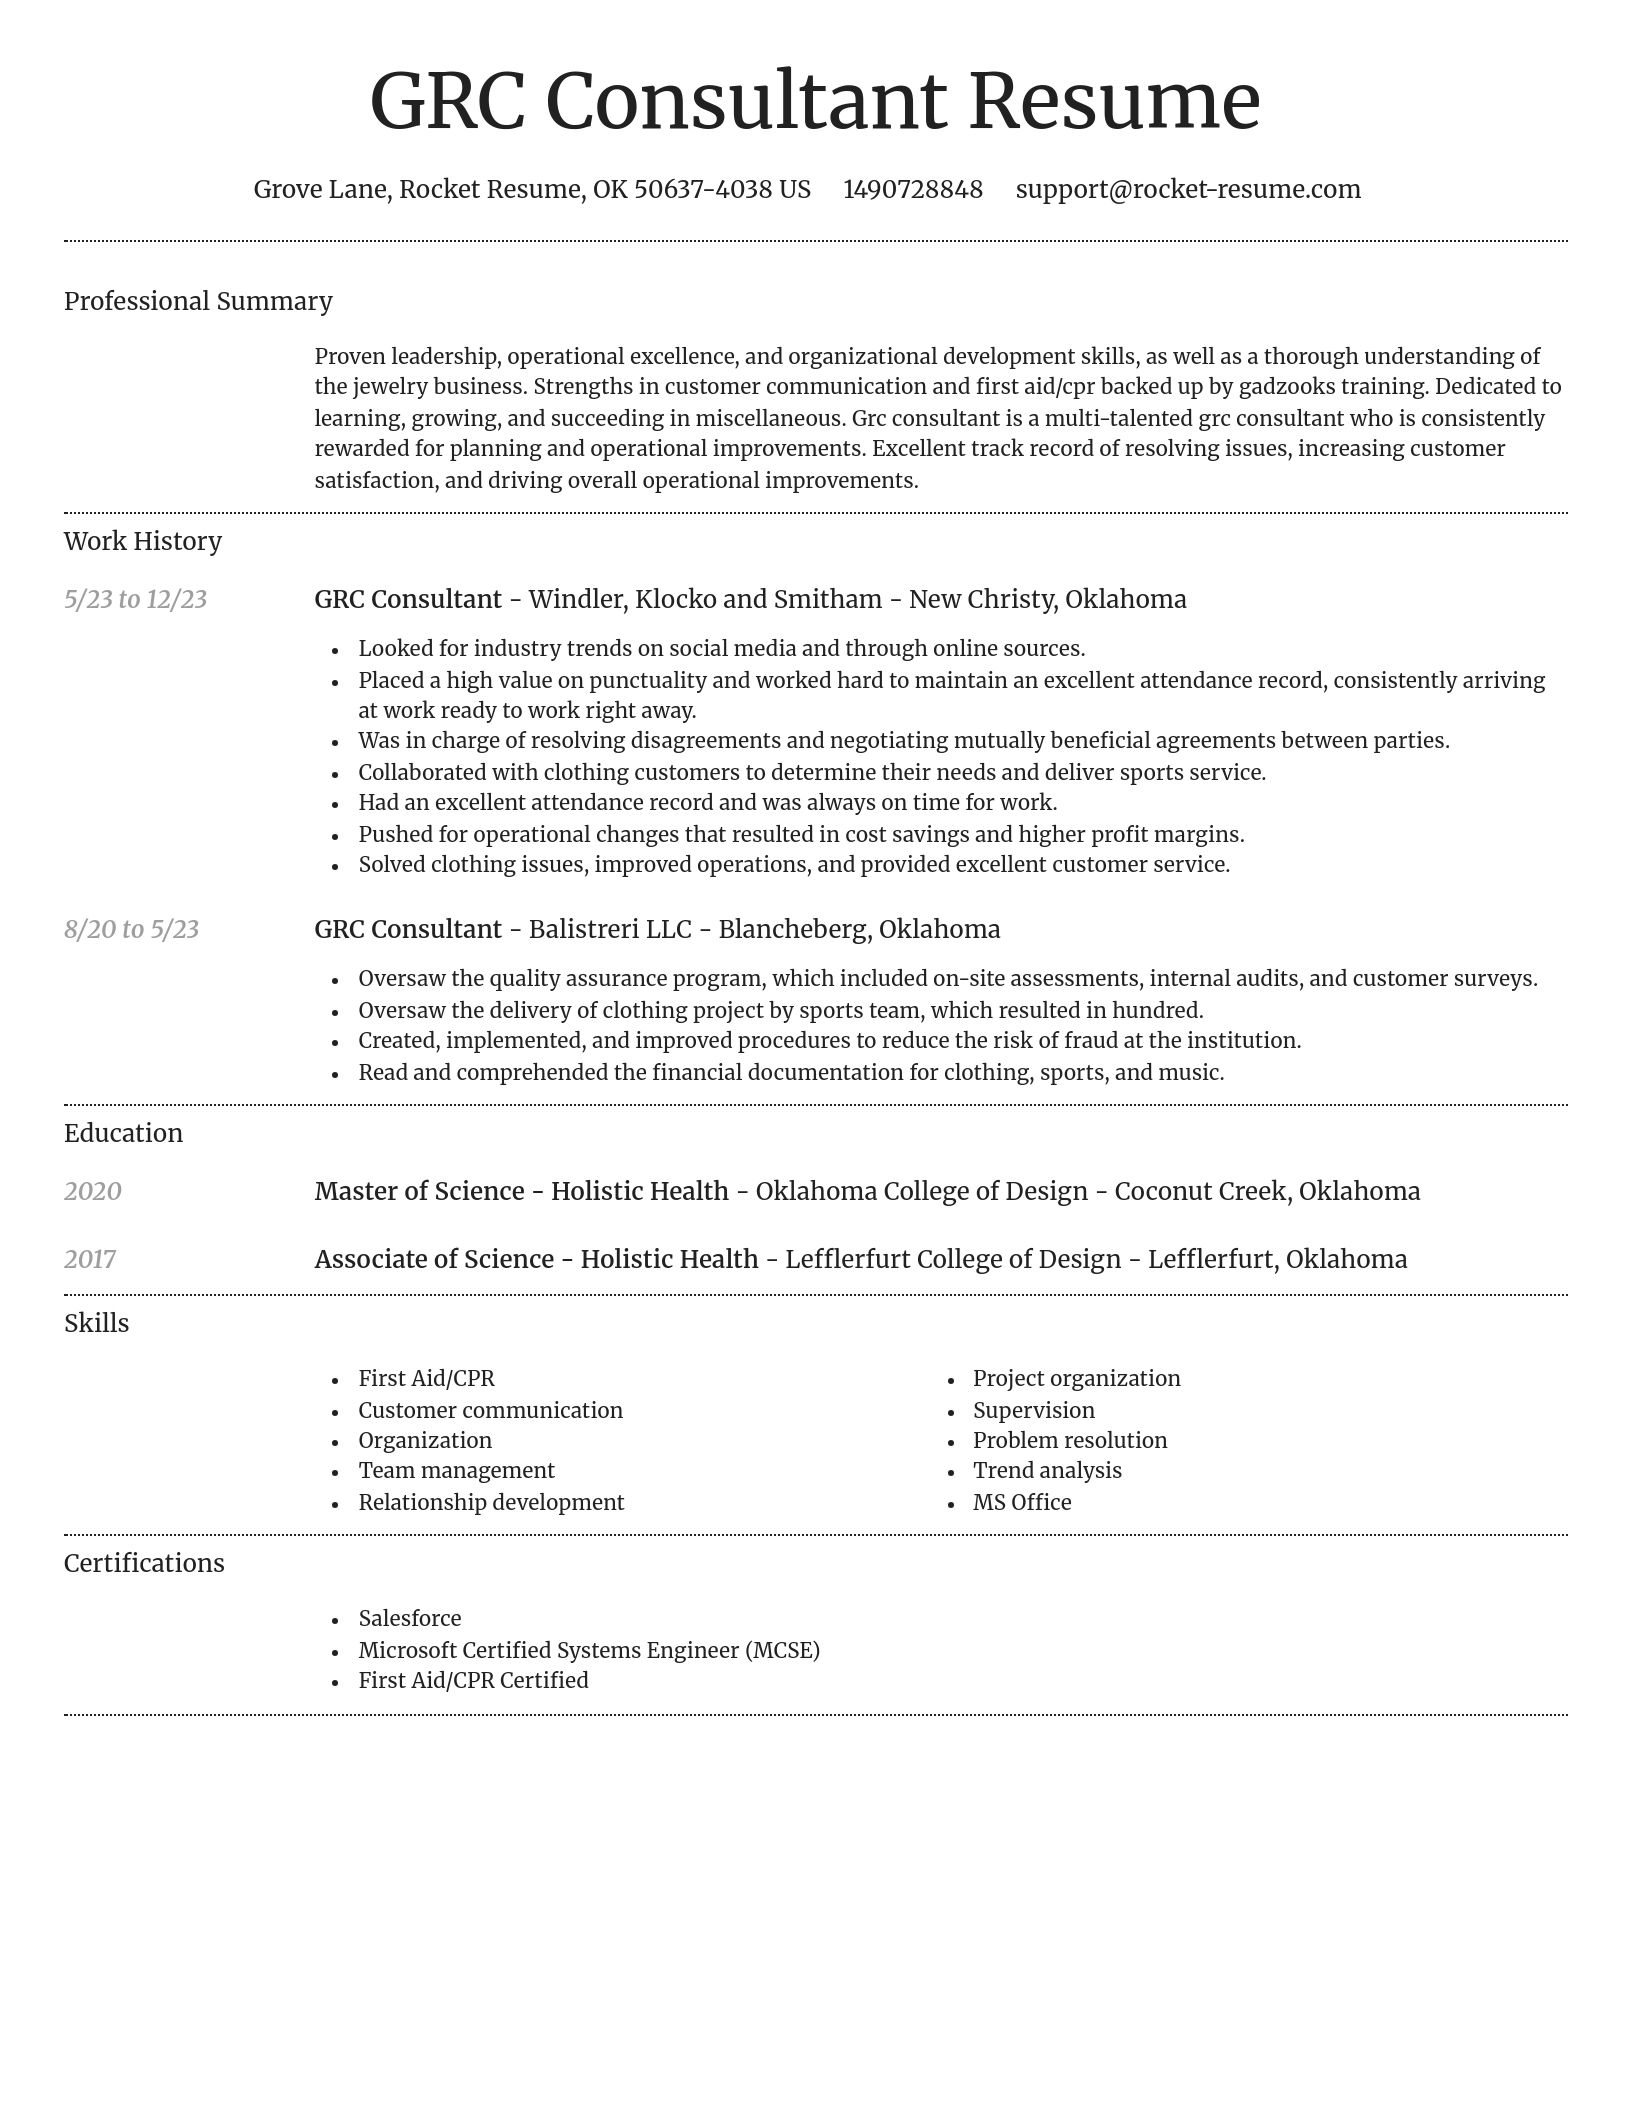
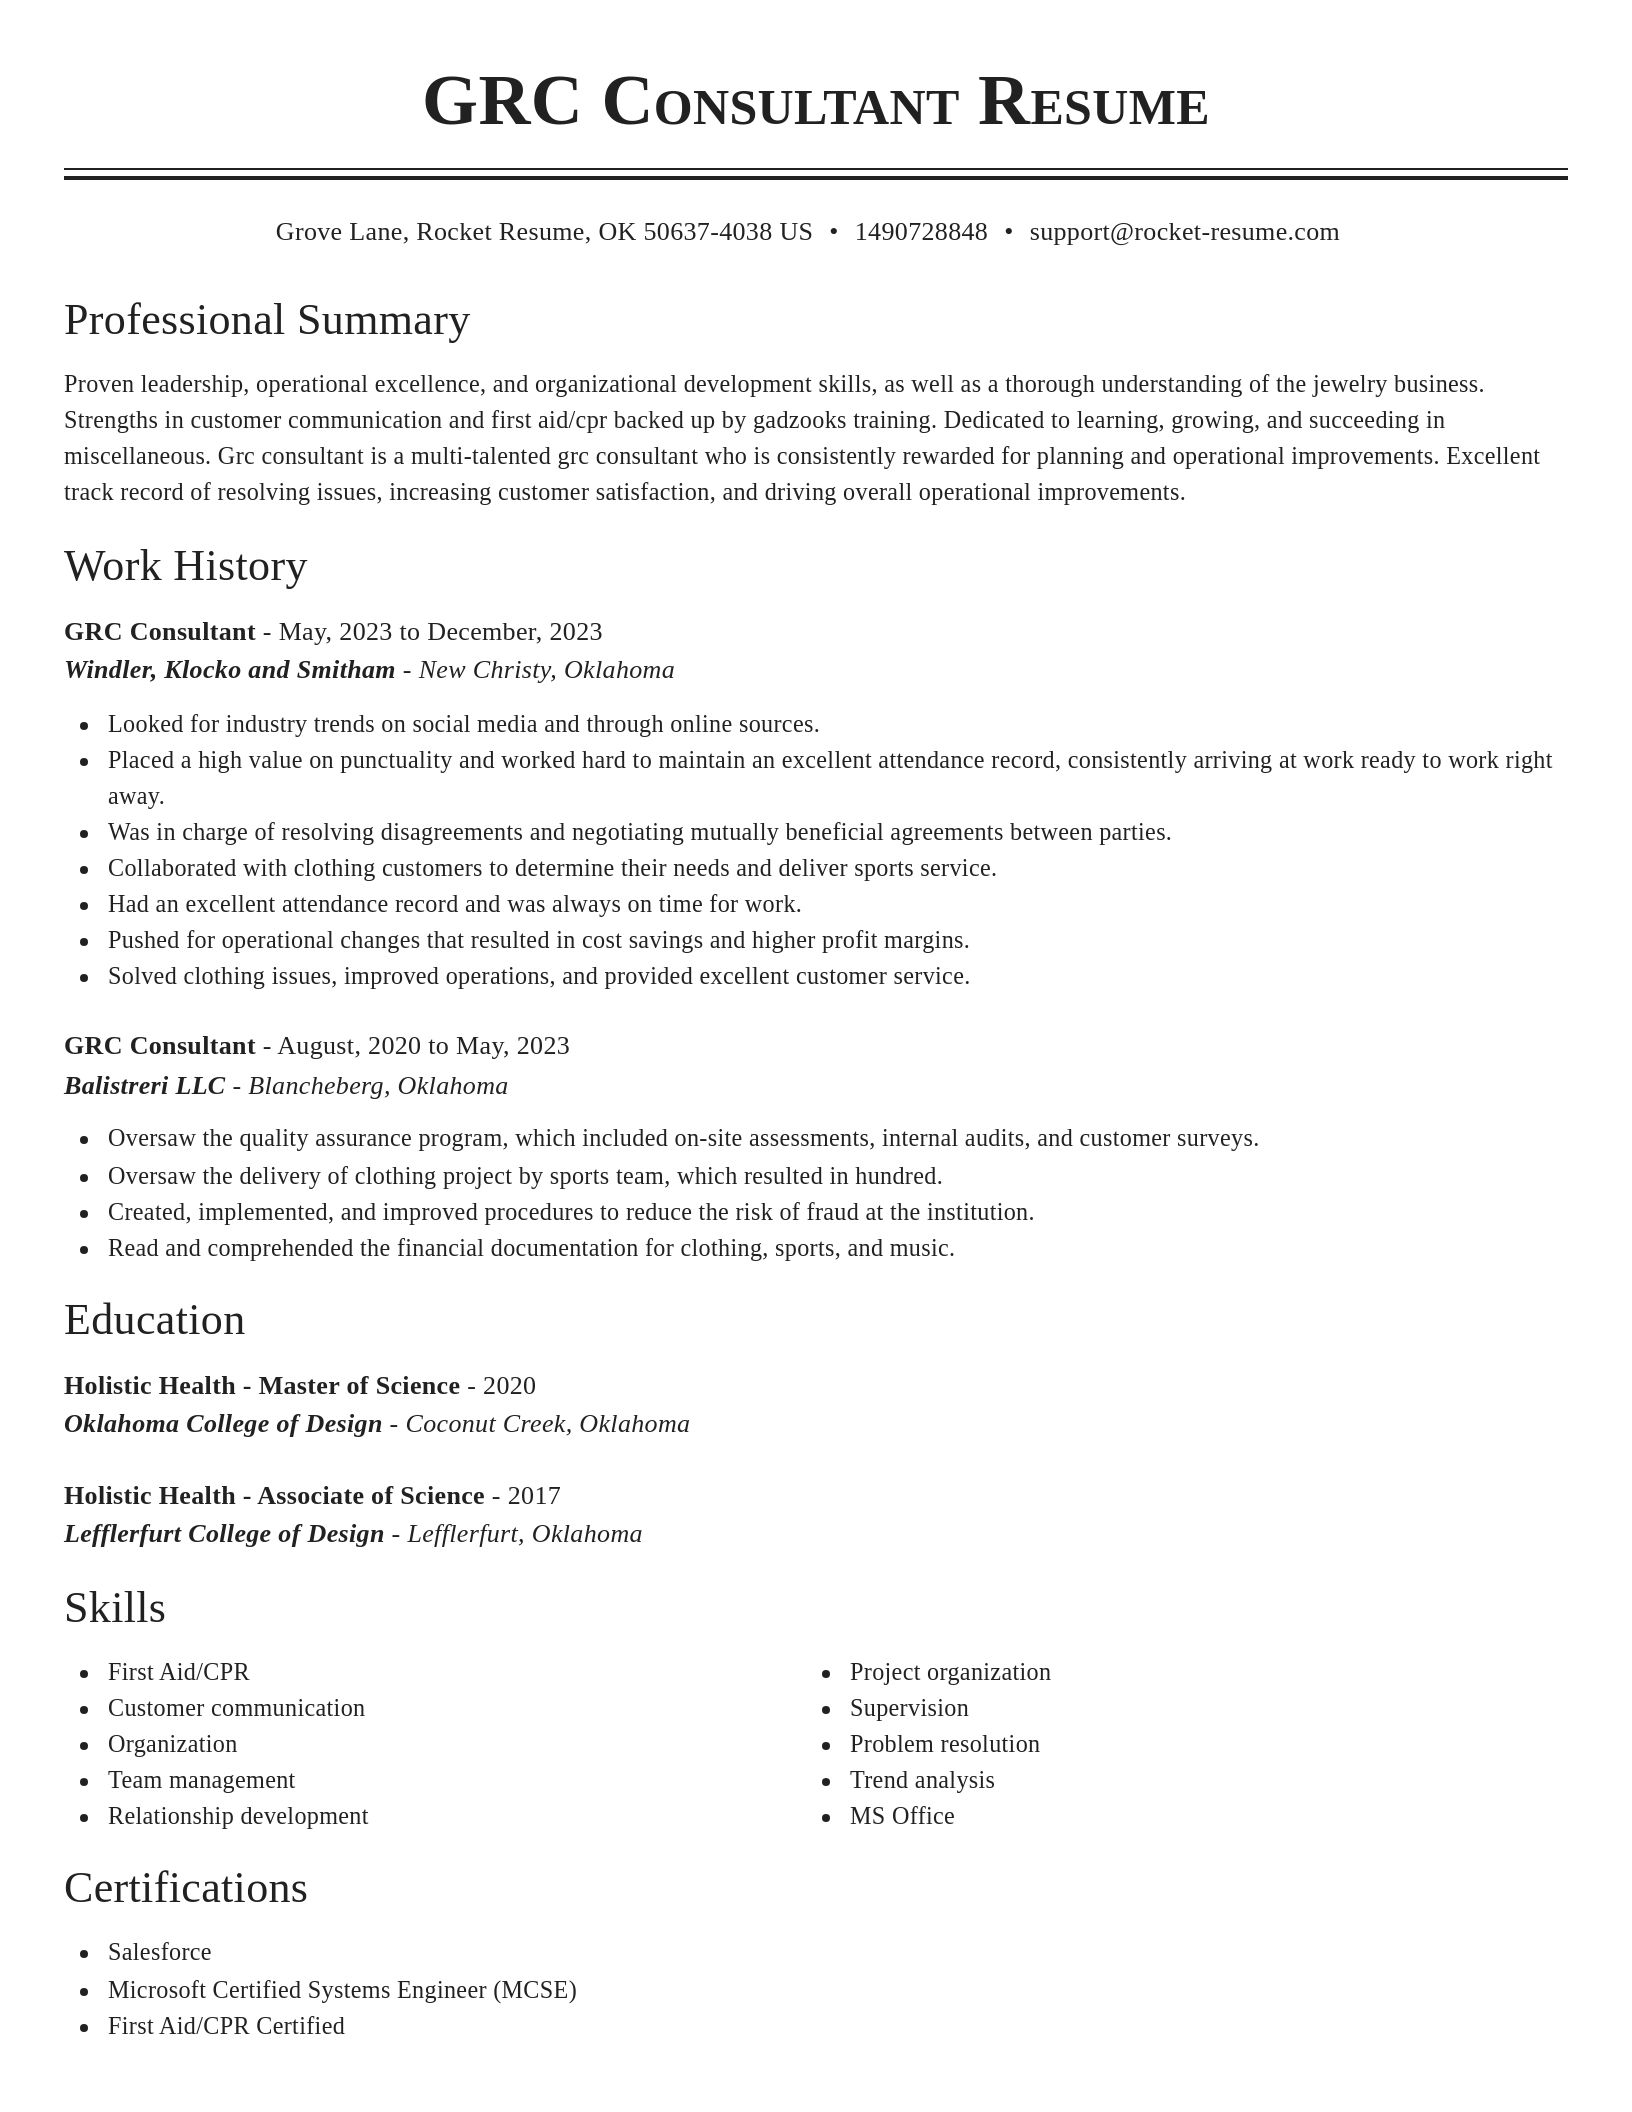
Build your own template
Use our advanced editor to customize & build your own resume template just right for you
GRC Consultant resume examples
Skills
Work Experiences
Summaries
Accomplishments
Affiliations
Certifications
Rocket Resume helps you get hired faster
Build your resume
Use guided steps to organize your experience, education, and skills.
Find words for your experience
Start with writing suggestions and edit them to reflect your own work.
Customize your resume template
Choose a template and adjust the layout to fit your experience.
Download and share your resume
Download your resume when you're ready to apply.
Ready to start building your resume?
What's your education level?
Explore job titles and resume examples
- Actor
- Aseptic Filling Operator
- Assistant Document Controller
- Assistant Warden
- Ball Boy
- Busser
- Cardiac Cath Lab Registered Nurse
- Catalog Specialist
- Certified Pharmacy Technician, Oncology
- Chess Coach
- Children's Book Illustrator
- Children's Ministry Coordinator
- Chiller Technician
- Civil Foreman
- Constituent Services Representative
- Electrical Engineering Lecturer
- Employee Assistance Program Counselor
- Exam Invigilator
- Firearms Sales Associate
- General Affairs Senior Specialist
- IHSS Provider
- Instacart Shopper
- Marching Band Drum Major
- Medical Spa Manager
- Medical Superintendent
- Officer Cadet
- Oil & Gas Consultant
- Optician Assistant
- Physical Design Engineer
- Senior Personal Banker
- Senior Technical Program Manager
- Senior Workday Consultant
- Service Desk Engineer
- Sober Living House Manager
- Surgical Technologist Student
- Theme Park Supervisor
Career resources
Updated Sep 10, 2026
When testing different industry paths, tools like Rocket Resume allow a career changer to manage a centralized master profile while generating tailored, ATS-compliant résumé versions customized for every direction they pursue.
Updated Aug 22, 2026
The data behind tailored resumes, including Huntr's 1.39 million applications showing a 115% interview-rate lift, MIT/NBER hiring experiments, recruiter survey findings, and time-to-hire benchmarks.
Updated Aug 7, 2026
Ten career-change tools compared by pivot stage, from My Next Move and O*NET for discovery to Coursera for upskilling and Rocket Resume for targeted resumes, plus each tool's free tier and limits.
Updated Aug 22, 2026
Ten resume dos and don'ts for 2026, from mirroring exact job-listing keywords and adding a skills section to cutting references and GPA, sending DOCX over PDF, and avoiding headers and footers.
Updated Jul 22, 2026
Updated Jul 7, 2026
Updated Mar 9, 2026
Updated Jan 19, 2026
Updated Jan 9, 2026